Google Authenticator
3.8ToolsUpdated October 17, 2026
Screenshots
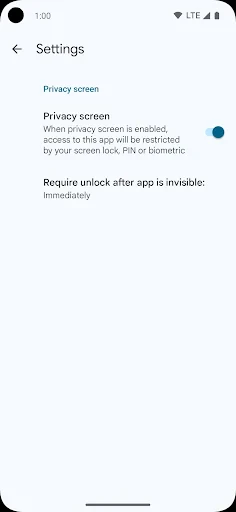
 Analysis by Mobexer
When I decide whether a security app is worth installing, I start with a simple question: does it make safer habits easier without creating a new daily chore? Google Authenticator is a focused tool for adding a second check when you sign in. It is free, so trying it does not require a purchase decision; its value comes from whether the extra step fits the accounts you use and the way you manage access.
What you get without paying
Google Authenticator is a free app from Google LLC in the tools category. It has been available since March 21, 2012, and is rated for everyone. Its average rating is 3.8 from around 627,000 ratings, with over 100 million installs. Those figures show that it is widely used, but they do not tell me whether it suits a particular person; the practical question is whether you want codes on your phone and are comfortable planning for a lost or replaced device.
There is no price to weigh against a paid plan here. I would judge its value by the protection it helps add to accounts that support authenticator codes, and by the small amount of attention it asks from me at sign-in. That makes it an easy option to try if you already want this kind of verification, though free access alone is not a reason to move every account into it.
What the extra sign-in step actually does
In the realm of cybersecurity, where our digital lives are constantly at risk, Google Authenticator stands as a trusty sidekick. It's like having a bouncer for your online accounts, making sure only the right folks get in. Let's dive into what makes this app a must-have for anyone who treasures their online privacy.
What’s the Deal with Google Authenticator?
Picture this: you’ve got a password, and you think it’s rock solid. But let’s face it, passwords can be cracked, phished, or just straight-up guessed. Google Authenticator adds an extra layer of security by generating a time-based one-time password (TOTP) that changes every 30 seconds. It’s like having a secret handshake that only you and your account know.
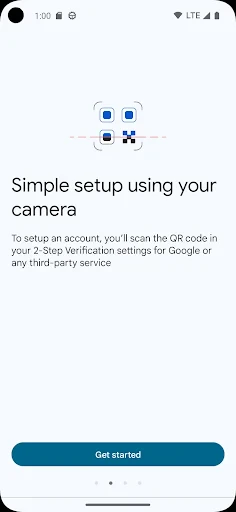
A time-based code is useful precisely because it is separate from the password: knowing one does not automatically supply the other. When a service offers this method, you scan its setup QR code to pair the account with the app. After setup, the app produces a short-lived code for sign-in. I see this as a practical middle ground: it takes more effort than using only a password, but it does not depend on waiting for a text message to arrive.
Setting Up – Easier Than Pie!
Setting up Google Authenticator is a breeze. You download the app, scan a QR code from your account's security settings, and boom, you’re fortified with two-factor authentication (2FA). The app doesn’t require an internet connection to generate codes, so you can feel secure even when you’re off the grid.
Fresh From the Newsroom
Google Play Services: The Android App That Works Best Unnoticed
Google Photos: Dominating the Mobile Photography Scene
How Booking.com Shapes Modern Travel Habits
What You Give Up When You Switch to Fortnite
How Gallery is Transforming Mobile Photography
How MobiOffice: Word, Sheets, PDF Masters iOS and Android Updates
A useful setup habit is to finish the account’s own recovery steps before you leave its security page. Save any recovery codes the service provides somewhere separate from your phone, and check that you can reach the account’s recovery options. That preparation matters because a working authenticator code is not the same thing as a complete recovery plan. If you are changing phones, do not erase or trade in the old one until you have confirmed that your accounts can be moved or recovered.
In an ordinary week, I might sign in to an email account from a laptop I do not use every day. I enter the password, open the authenticator on my phone, and type the current code. If I am travelling without a reliable data connection, the code-generation step still works offline. That convenience does not make every sign-in risk-free, but it avoids depending on a text arriving at the right moment.
Security and Simplicity Rolled Into One
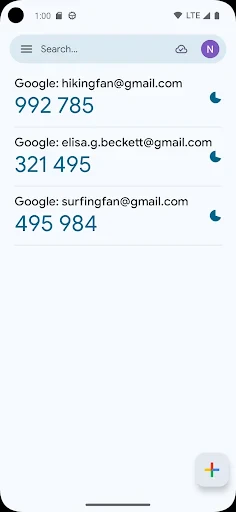
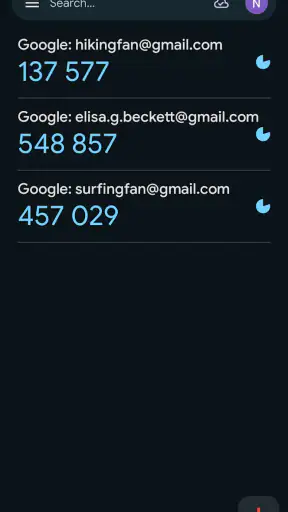
One of the things I love about Google Authenticator is its no-frills approach. It doesn’t bombard you with unnecessary features or ads. The interface is clean and straightforward. You open the app, and there you have it: a list of your accounts with the corresponding codes. It’s this simplicity that makes it so user-friendly.
That uncluttered design is especially helpful when you have several accounts and need to find the right entry quickly. I would give each entry a clear account label during setup, rather than relying on memory or leaving multiple similar names indistinguishable. Before using a code, I also check that I have selected the account I meant to access; a code from a different entry will not help, even if it looks just as valid.
The app’s role is deliberately narrow: it generates codes, while the website or service you are signing in to decides whether to accept them and handles account recovery. That division is worth understanding. If a service offers a passkey or another sign-in method that better suits your devices and recovery preferences, it may be more convenient than entering a code by hand. For people who prefer a straightforward second factor that works across services supporting authenticator codes, this app keeps the process familiar.
Why It’s a Keeper
The peace of mind that comes with knowing your accounts are secure is invaluable. Google Authenticator’s reliability and ease of use make it a staple in my digital toolkit. Whether you’re tech-savvy or a newbie, this app is designed for everyone.
I find it most useful for accounts where losing access would cause real disruption, such as a primary email account or an account used to manage other services. The benefit is not limited to signing in: protecting an email inbox can also make it harder for someone who knows a reused password to use that inbox to reset other accounts. I would prioritize accounts based on the consequences of losing them, then add verification to the ones that support it instead of treating every login as equally urgent.
There is a small but important trade-off in daily use: codes are quick, yet they ask me to keep my phone nearby and pay attention to the countdown. If a code expires while I am switching between screens, I simply wait for the next one rather than repeatedly submitting an old entry. I also avoid sharing a code with someone who contacts me unexpectedly; a one-time code is still a secret, not a routine customer-support detail.
Where it sits among sign-in alternatives
Compared with SMS verification, an authenticator code does not rely on a text reaching the same phone number at sign-in, and it can be generated without an internet connection. That is useful when mobile reception is poor. SMS may still be simpler for someone who does not want another app, while a passkey can be smoother for people whose devices and services support that approach. The best option depends on the service, the devices you use, and how confidently you can recover access if something goes wrong.
Some people also prefer an authenticator built into a password manager, so passwords and codes are kept in one workflow. That can reduce app switching, but it also concentrates more sign-in information in one place. I would choose based on the risk I am trying to manage: keeping codes separate from passwords can create a useful separation, while a carefully secured password manager may be more convenient for someone who values a single organized system. Google Authenticator is the simpler fit when the priority is a dedicated code generator rather than an all-in-one sign-in tool.
If you are setting up verification on a shared or borrowed device, pause before scanning the QR code: the phone holding the authenticator becomes part of the sign-in process. Use a device you control, and make sure you understand the service’s recovery route before enabling the extra step. This is a modest precaution, but it prevents a common mismatch between securing an account and retaining practical access to it.
Room for Improvement?
No app is perfect, and Google Authenticator is no exception. The lack of a backup feature can be a bit nerve-wracking. If you lose your phone, you lose your access codes. There’s no cloud sync, which means transferring your codes to a new device requires a bit of a workaround. But hey, that’s a small price to pay for added security, right?
That limitation changes how I would use it. Before replacing a phone, I would check each important service’s recovery method and move or reconfigure its authenticator access while I still have the old device. If I cannot keep both devices available during the change, I would first make sure I have the service’s recovery codes or another supported route. The exact steps depend on each account, so I would not assume that moving the app alone completes the transfer.
This is also where a different option may be a better fit. If you regularly change devices, want a more guided recovery experience, or would rather keep codes synchronized as part of another secure tool, compare those workflows before choosing. A backup convenience can make recovery easier, but it also changes where account secrets are stored and what you must protect. I would not trade one setup for another without understanding that balance.
Who gets the most value from it?
I would recommend it to someone who wants a direct, no-cost way to generate sign-in codes, uses services that support authenticator apps, and is willing to keep a sensible recovery plan. It is particularly practical for people who travel, have unreliable mobile reception, or want a verification method that does not depend on receiving a text at the moment they log in.
I would hesitate to recommend it as the only plan to someone who often loses phones, shares devices, or does not feel comfortable managing recovery codes. The same goes for a person who prefers passkeys and already has a dependable way to use them across their devices. In those cases, another sign-in method may be less awkward, provided it is available for the accounts that matter and the recovery process makes sense to that person.
My verdict is that the app earns its place by doing one job simply, not by replacing every form of account security. Free access makes it easy to try, and the everyday code workflow is straightforward once accounts are enrolled. The main cost is responsibility: I have to protect the phone and think ahead about recovery. If that trade-off suits you, Google Authenticator is a sensible tool to keep; if device loss would leave you stuck and you do not want to plan around it, choose a method with a recovery workflow you trust more.
In conclusion, Google Authenticator is a straightforward, no-nonsense app that bolsters your online security with minimal effort. It’s like having a personal security guard for your digital life. Sure, it could use some enhancements, but as it stands, it’s a robust tool that does its job well. If you haven’t tried it yet, give it a whirl and see how it transforms your approach to online security.
FAQ
What is Google Authenticator and how does it work?
Google Authenticator is a security app used to generate verification codes for two-factor authentication (2FA) on your online accounts. Once you enable 2FA on a compatible service, you can use the app to scan a QR code or enter a setup key provided by the service. This links the app to your account, allowing it to generate time-based, one-time passwords (TOTP) that enhance your account’s security.
Is Google Authenticator available for both Android and iOS devices?
Yes, Google Authenticator is available for both Android and iOS devices. You can download it from the Google Play Store for Android devices and the Apple App Store for iOS devices. It’s a free app that can be easily installed and set up on most smartphones, providing an extra layer of security for your online accounts by generating time-sensitive codes for authentication.
Can I use Google Authenticator without an internet connection?
Yes, once Google Authenticator is set up, it does not require an internet connection to function. The app generates time-based codes that are synchronized with the server time on your device. This offline functionality ensures that you can still access your accounts securely even when your device is not connected to the internet, making it a reliable tool for two-factor authentication.
What should I do if I lose my device with Google Authenticator installed?
If you lose your device with Google Authenticator installed, you should immediately secure your accounts. It is recommended to keep backup codes provided by the services where you’ve enabled two-factor authentication. Additionally, you can try to restore your Google Authenticator data on a new device using your Google account, if a cloud backup feature is available, or contact the service provider for further assistance.
How can I transfer Google Authenticator codes to a new phone?
To transfer Google Authenticator codes to a new phone, you can use the app’s transfer feature. On your old device, select the accounts you want to transfer and generate a QR code. Then, on your new device, open Google Authenticator, and use the 'Import existing accounts' option to scan the QR code. This transfers your 2FA codes securely to your new phone, ensuring continued access to your accounts.
Download