Imprivata ID
3.0MedicalUpdated October 5, 2026
Screenshots
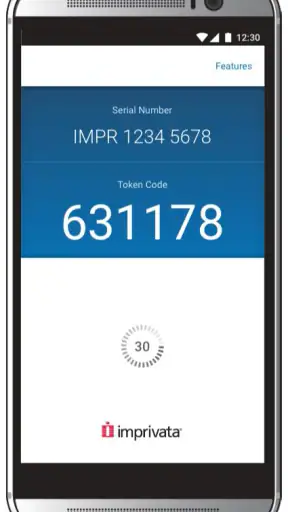
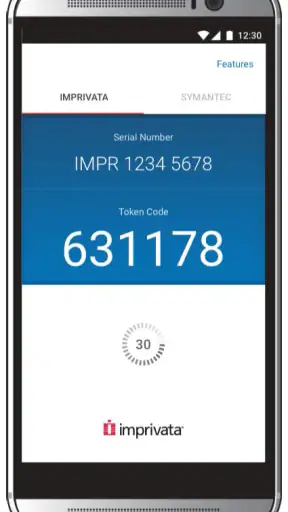
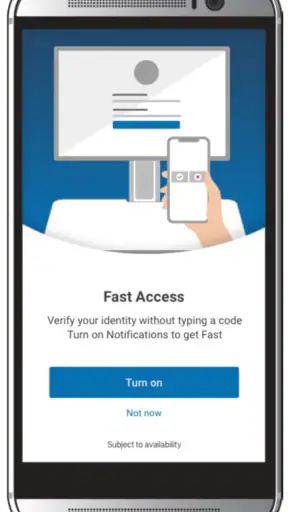
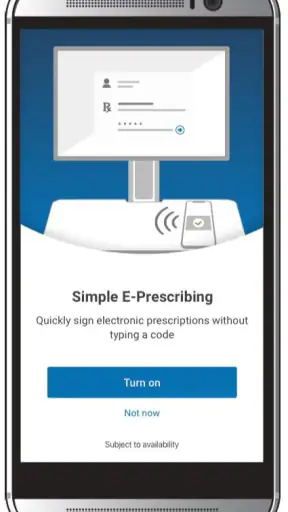
Pros
- Quick push approvals make sign-ins convenient.
- Supports biometric verification on compatible devices.
- Works with multi-factor authentication workflows.
- Helps reduce reliance on passwords.
- Designed for enterprise security requirements.
Cons
- Requires an organization-issued Imprivata account.
- Features may be limited outside supported workplaces.
- Push approvals depend on an internet connection.
- Device changes may require account re-enrollment.
- Some users may find setup steps confusing.
 Analysis By Mobexer
In a hospital or clinic, a few seconds spent proving who you are can become surprisingly important. Imprivata ID is built for that environment: it is a medical authentication app from Imprivata, Inc., intended to support secure access and smoother clinical workflows for professionals. I see it less as a general-purpose security app and more as one part of an organization’s wider identity system.
That distinction matters before you install it. This is not the kind of app I would choose to protect personal photos, replace a password manager, or add a general login layer to every account I use. Its usefulness depends heavily on whether a hospital, clinic, or other supported workplace has configured Imprivata’s authentication service for its staff. Without that connection, the app has little value for an ordinary phone user.
The app is free to download and available for Everyone, with support beginning at Android 6.0. It has been available since May 27, 2016, and the current Android release is 2026.1.1.144. Its presence on more than 500 thousand devices suggests that it serves a real workplace audience, although the average score sits at 3.0 from roughly 509 ratings, so the experience is clearly not frictionless for everyone.
Where Imprivata ID fits in a clinical workflow
My first impression is that Imprivata ID makes the most sense when authentication is part of a larger clinical routine rather than an isolated phone task. A nurse moving between workstations, a doctor checking information during rounds, or a staff member signing in to a protected service may need a quick way to confirm identity. In those situations, reducing unnecessary steps can be genuinely useful, provided the employer’s setup is working properly.
The important word is “configured.” Installing the application alone does not turn a phone into a universal medical login tool. Your organization normally needs to enroll you and connect the app to the relevant authentication environment. That means the right first step is usually to follow workplace instructions, not to experiment with random settings or assume that any medical portal will recognize it.
This also explains why reviews of the app can be mixed. A consumer app is usually judged almost entirely by what happens after installation. With Imprivata ID, the visible phone experience is only one piece of the process. Enrollment, account status, device replacement, network conditions, and the policies chosen by an employer can all affect how convenient the app feels.
A realistic shift scenario
Imagine arriving for an early shift and needing access to a workstation before reviewing patient information. If your organization has already enrolled your device, the app may serve as a practical confirmation step instead of forcing you through a longer manual process each time. The benefit is not flashy; it is the reduction of small interruptions during a busy day.
Now imagine the same situation after changing phones. The app may still be installed, but that does not automatically mean the new device is trusted. You may need help from your organization to enroll it again or restore access. This is one of the most important practical points: the app cannot replace your employer’s account and device-management process.
For a clinician, that dependency is both a strength and a weakness. Centralized control can be appropriate when access to sensitive systems must be managed carefully. At the same time, it means a problem may not be solvable from the app itself. If enrollment fails or your account is unavailable, the correct solution may be contacting an administrator rather than reinstalling repeatedly.
Why the medical context changes the review
In ordinary authentication apps, inconvenience usually means losing a few minutes or having to repeat a login. In healthcare, access has a more complicated balance. Staff need efficient workflows, but protected systems also require careful identity checks. I therefore judge Imprivata ID less by how many buttons it has and more by whether it supports a controlled process without encouraging unsafe shortcuts.
The app’s stated purpose is closely tied to secure authentication and clinical workflows, so I would not treat it as a casual productivity download. A person deciding whether to use it should first ask whether their workplace specifically uses Imprivata technology. If the answer is no, another authenticator or the organization’s own access method will almost certainly be more relevant.
Trust, controls, and the moments that deserve attention
When I review an app connected with medical work, trust is not just about a polished interface. I want to know what role the app plays, who controls access, and what happens when something changes. Imprivata ID presents itself as an authentication component rather than a place to store or manage clinical records. That is a useful boundary, but it does not remove the need to understand the surrounding account and device policies.
The most reassuring aspect of this type of design is the separation between the phone application and the organization’s protected services. The app is not something I would expect to function independently as a medical record viewer. Its purpose is to help establish identity within a configured system. That narrower role can reduce confusion, especially for staff who might otherwise assume that every medical app directly handles patient information.
Still, the sensitive moments are easy to identify. Enrollment is one. Device replacement is another. Losing a phone, changing a phone number, resetting a device, or leaving an organization can all affect access. I would want clear workplace instructions for each of these situations before relying on the app during a shift.
There is also a practical distinction between authentication and authorization. Even if the app successfully confirms who you are, your organization may still decide which systems or areas you can enter. In other words, a successful app interaction does not necessarily mean every clinical resource is available. Access rights remain a workplace matter.
What I would check before trusting it at work
Before depending on Imprivata ID, I would confirm the enrollment process with the organization’s support team and make sure I know the backup procedure. I would also check whether the workplace expects the phone to have a screen lock, current system software, or other security settings. Those requirements may come from the organization rather than the app, but they directly affect the experience.
- Confirm the correct enrollment route instead of assuming installation is enough.
- Keep the phone available during the parts of a shift when authentication may be required.
- Learn how to report a lost or replaced device before an emergency occurs.
- Ask which support channel handles failed enrollment or locked accounts.
- Separate personal phone troubleshooting from workplace access troubleshooting.
These steps are not glamorous, but they are more useful than simply reading a short store description. They also protect against a common mistake: treating a workplace authentication tool like a normal app that can be deleted and reinstalled without consequences.
Permissions, data, and visible choices
I am deliberately cautious about making claims beyond what can be observed in the app’s role and the controls presented by the organization. Authentication apps operate around account identity and device trust, so I would read the app’s permission prompts carefully and avoid granting anything that does not appear relevant to the enrollment or authentication task.
I would also review the privacy and data explanations shown during setup or in the relevant store and workplace materials. The safest habit is to distinguish between information needed to identify a device or account and information that is merely convenient for another purpose. If a prompt is unclear, I would pause and ask the organization’s administrator rather than approving it automatically.
That approach is especially important on a personal phone. Employees may be comfortable using their own device for authentication, but they should understand what the workplace requires and what remains under their personal control. The app’s presence on a phone does not, by itself, explain every policy applied by an employer’s identity platform.
For me, trust comes from visible choices and clear responsibility. I want to know when an account is being enrolled, how a device can be removed, and whom to contact if access must be revoked. If those instructions are easy to find, the experience feels more manageable. If they are hidden in internal procedures, the app can feel confusing even when the underlying security design is sensible.
Where the usual alternatives may be better
For personal accounts, a general authenticator app is usually a better fit. Those tools are designed for individuals managing multiple online services, often with a clearer focus on personal account recovery and broad compatibility. A password manager may be more appropriate when the main problem is storing credentials securely. Imprivata ID is not a substitute for either option.
For a medical organization, the comparison is different. An employer may prefer a unified identity platform because it can manage staff access centrally and connect authentication with clinical workflow requirements. A generic authenticator might be simpler for one employee, but it may not fit the organization’s chosen systems or support process.
This is where I see the app’s main trade-off. It can be more relevant than a general alternative when your workplace has adopted Imprivata’s environment. Outside that environment, its specialized nature becomes a disadvantage. The best choice is therefore determined less by personal preference and more by the access system your organization already operates.
Daily usability, limitations, and who should choose it
In everyday use, I would expect the app to be most valuable when it stays in the background and helps authentication happen without distracting from clinical work. The ideal experience is brief: open or respond when needed, confirm identity through the organization’s process, and return to the task at hand.
That convenience should not be confused with universal simplicity. A staff member may still encounter delays caused by account enrollment, a new device, an unavailable phone, or an organization policy. Those are not necessarily failures of the app’s interface, but they are part of the real user experience. A review that ignores them would give clinicians an unrealistic expectation.
The average rating of 3.0, based on around 509 ratings and 234 written reviews, reinforces my cautious view. It indicates that the app has not delivered a consistently smooth experience for every user. I would not interpret that score as proof that the app is unsuitable, because workplace configuration can strongly influence results. I would interpret it as a reason to prepare for support and enrollment issues rather than assuming everything will work instantly.
Another limitation is dependence on a phone that is available and usable at the right time. A low battery, damaged device, changed handset, or forgotten screen-lock method can become an access problem. If your workplace permits or provides another authentication route, learn it in advance. If it does not, keep the organization’s support instructions accessible somewhere other than the app itself.
Who will get the most from it
Imprivata ID is best suited to medical professionals whose employer explicitly uses Imprivata authentication and has given them enrollment instructions. It can also suit staff who move frequently between protected clinical workstations or services and want authentication to fit more naturally into that movement.
I would recommend it to a clinician who values a workplace-managed process and is comfortable following organization-specific security rules. The app’s greatest advantage is not independent functionality; it is its place inside a controlled clinical access workflow.
I would not recommend downloading it merely because it sounds medical or secure. A student, patient, caregiver, or general smartphone user is unlikely to benefit unless an institution has told them to use it. Likewise, someone looking for a personal two-factor authentication tool should start with an app designed for broad personal use.
Questions I would resolve before installation
The first question is whether your employer actually supports it. If nobody in your organization has mentioned Imprivata ID, installation alone probably will not create access. Ask the help desk or identity administrator for the official enrollment instructions.
The second question is what happens if your phone is lost or replaced. I would want to know how quickly access can be disabled, how a new device is enrolled, and whether another sign-in method exists. This is more important than learning the app’s basic interface because it determines how you recover from the situations most likely to interrupt work.
The third question concerns personal-device use. If you are using your own phone, ask what security settings are required and what information the organization needs for enrollment. The goal is not to avoid workplace security, but to understand the boundary between your device and your employer’s account controls.
The fourth question is support. If authentication fails during a busy shift, should you contact local IT, a clinical systems team, or an identity administrator? Knowing the answer can prevent repeated reinstalls and wasted time. Authentication problems are often account or policy problems, not ordinary app bugs.
Finally, consider whether your phone is reliable enough for the role. If you regularly work with a nearly empty battery, poor connectivity, or a device that you cannot keep with you, ask whether the organization offers another approved method. A secure tool is only practical when it is available at the moment access is needed.
My cautious verdict on Imprivata ID
I see Imprivata ID as a specialized workplace tool with a clear audience rather than a broadly useful medical app. Its purpose makes sense: help medical professionals authenticate within a controlled environment and reduce unnecessary friction during clinical work. When an organization has configured it properly, that focused role can be valuable.
My recommendation comes with an important condition: judge the complete access process, not just the application. Enrollment, device changes, account recovery, support, and workplace policy shape the experience as much as the phone interface does. The app can be a useful link in that chain, but it cannot independently solve every access problem.
The free price and broad age classification make it easy to obtain, while support for Android 6.0 and later keeps it accessible on many older devices. However, availability should not be mistaken for suitability. This is for professionals whose organization has chosen the platform, not for anyone seeking a general security app.
After weighing its role, limitations, and trust considerations, I would install it when my hospital or clinic instructed me to do so and provided a clear enrollment path. I would keep a recovery plan ready, pay attention to permission and account prompts, and learn the lost-device procedure before relying on it. For that specific audience, it may make clinical authentication more manageable. For everyone else, a general authenticator or password manager is likely the more sensible choice.
FAQ
What is Imprivata ID used for?
Imprivata ID is a mobile authentication app designed to help users securely verify their identity when accessing supported business systems, applications, and services. It commonly works as part of a company’s multi-factor authentication or access-management setup. After enrollment, the app may approve login requests or generate a one-time security code, depending on how the organization has configured it.
How do I set up Imprivata ID after downloading it?
Installing Imprivata ID is only one part of the setup process. Your employer, healthcare organization, school, or system administrator normally provides enrollment instructions, such as a QR code, activation link, or registration process. You may need to confirm your identity and allow notifications. The app cannot usually be used independently without an account or an organization that supports Imprivata authentication.
Does Imprivata ID require an internet connection?
An internet or mobile-data connection may be required for enrollment, account synchronization, and receiving approval requests. In some configurations, Imprivata ID can generate a time-based passcode without continuous connectivity, but this depends on the organization’s security policy and the authentication method enabled for your account. If notifications do not arrive, check your connection, notification permissions, and device settings.
Is Imprivata ID safe to use?
Imprivata ID is intended to add an extra layer of protection beyond a username and password by requiring approval on a registered mobile device or by using a temporary verification code. Its security also depends on how your organization configures the service and how carefully you protect your phone. Use a screen lock, keep the app updated, never approve unexpected requests, and report suspicious activity to your administrator.
What should I do if I lose my phone or cannot access Imprivata ID?
If your phone is lost, replaced, reset, or unavailable, contact your organization’s IT or security support team as soon as possible. They can disable the old device, help you enroll a new one, or provide an approved alternative verification method. Avoid repeatedly attempting random codes or reinstalling the app without guidance, because these actions may not restore access and could trigger additional security restrictions.